GrapheneOS closes an Android VPN loophole before Google does
Source ↗
👁 0
💬 0
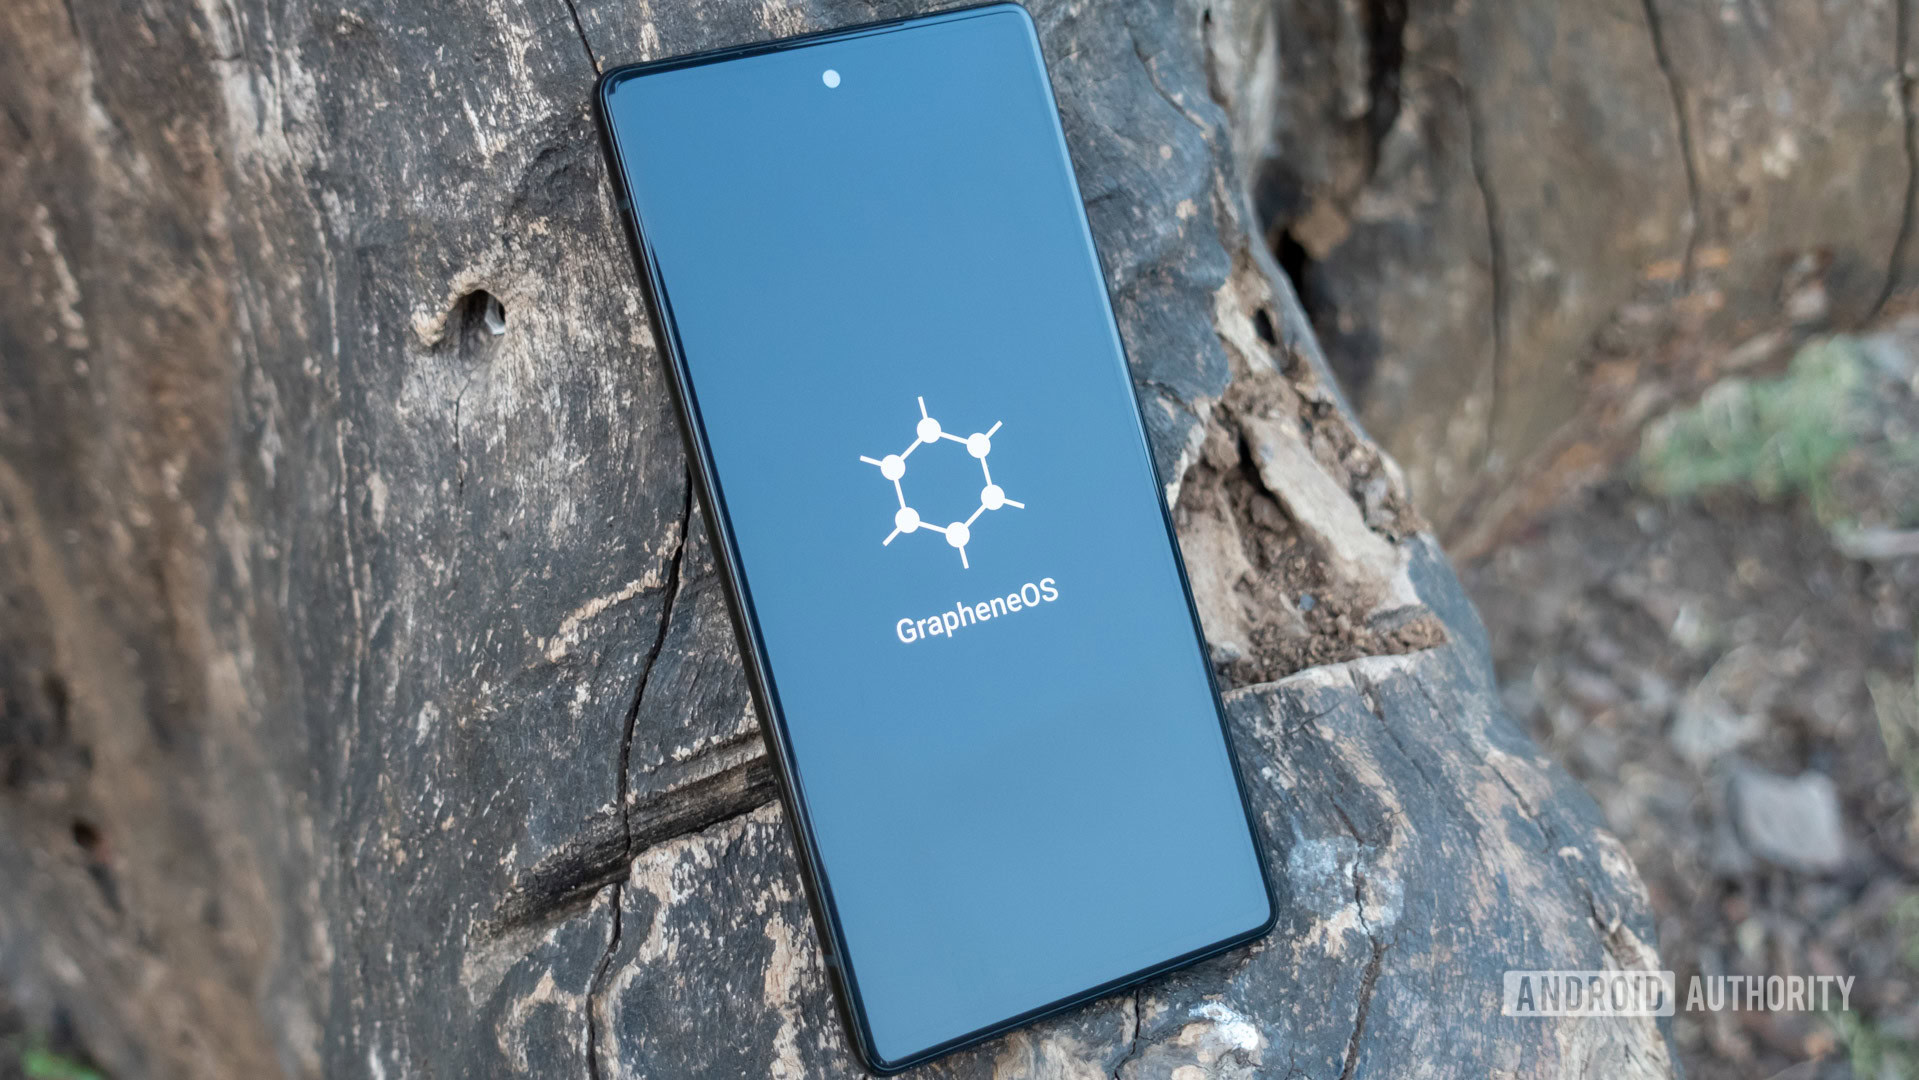
Credit: Calvin Wankhede / Android Authority
TL;DR
GrapheneOS has patched an Android 16 VPN flaw that Google reportedly decided not to fix.
The bug could let a malicious app leak small amounts of data outside an active VPN tunnel.
In extreme cases, that means it’s possible stock Android users could have their IP address leaked, even with strict lockdown controls enabled.
A VPN that can leak your location is a pretty big failure of the tech at the best of times, but it’s especially concerning
TL;DR
GrapheneOS has patched an Android 16 VPN flaw that Google reportedly decided not to fix.
The bug could let a malicious app leak small amounts of data outside an active VPN tunnel.
In extreme cases, that means it’s possible stock Android users could have their IP address leaked, even with strict lockdown controls enabled.
A VPN that can leak your location is a pretty big failure of the tech at the best of times, but it’s especially concerning
Also reported by 1 other outlet
Compare full coverage →- Google Releases Snapseed 4.0 for Android, iOSThurrott.com · May 8, 2026

Comments (0)